Incident Response

Incident Response

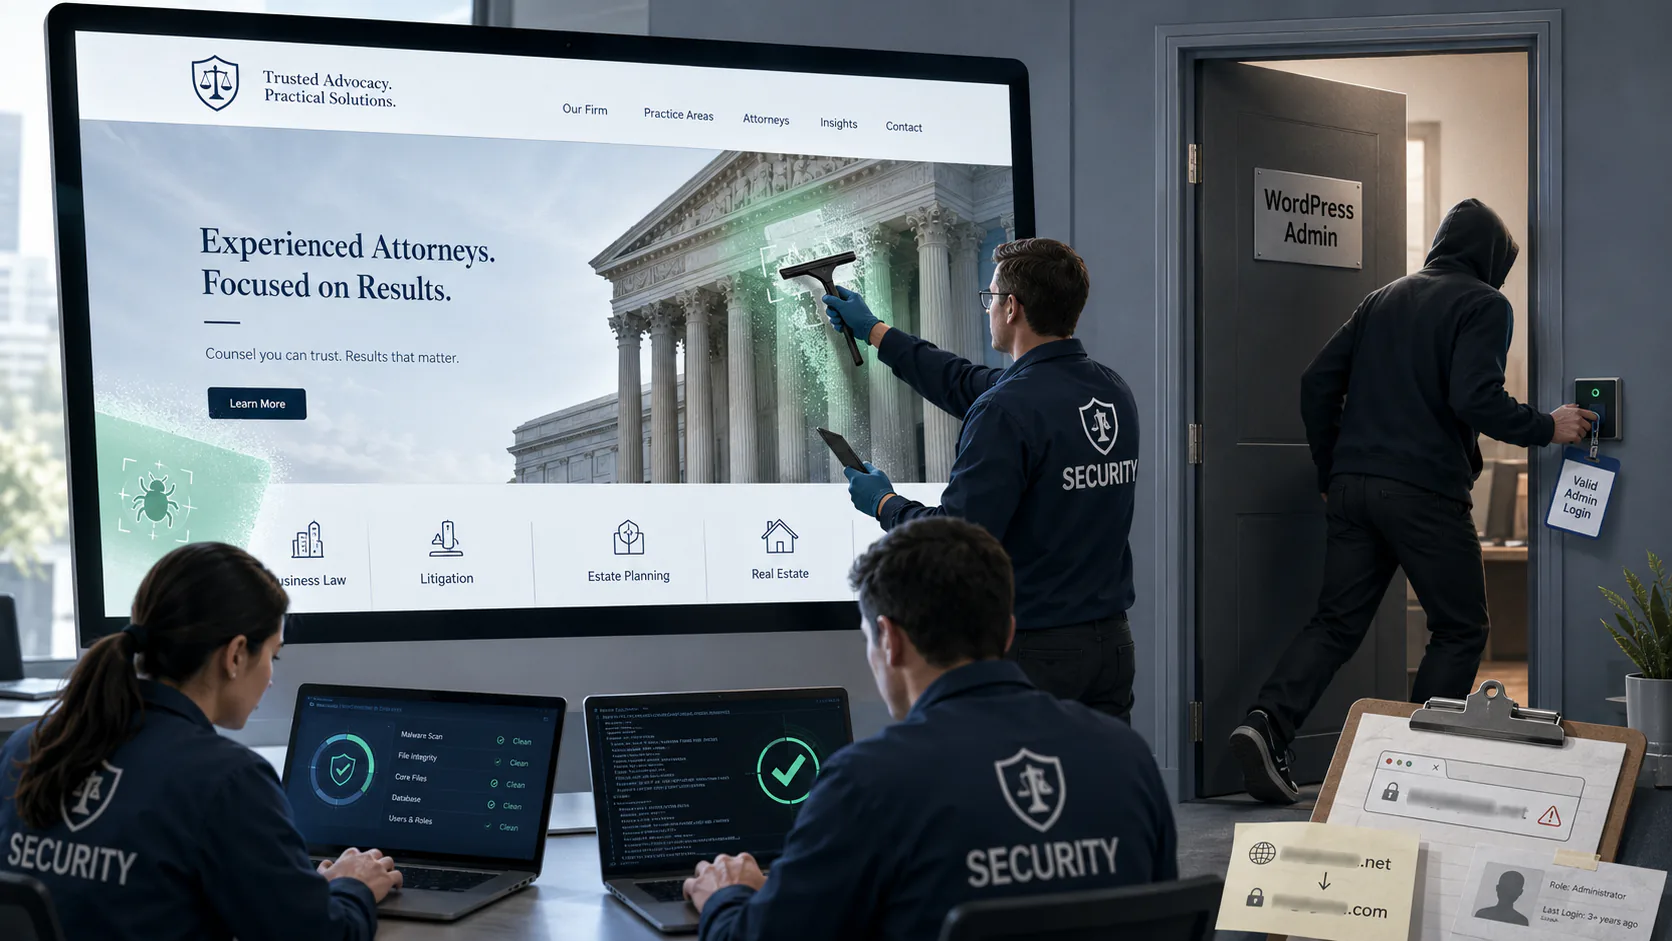
Case Study: No Backdoor Required

A law firm's WordPress site kept getting reinfected with ClickFix malware after every professional cleanup. The root cause was not a self-healing virus. It was a valid administrator login that was never rotated. Here is the full investigation.

Read Details
Incident Response

Case Study: The Keys Were Never Taken Back

A boutique advisory client's two WordPress sites were compromised through administrator access left over from the freelancer who built them: rogue admin accounts, gambling spam, and a file-manager backdoor. A full forensic remediation evicted the operator and cleaned and hardened both sites.

Read Details
Incident Response

Case Study: Blocked by Its Own Advertising

An established watch brand's Shopify store was blocked by Avast and AVG as dangerous. It looked like a hack, but a full forensic audit found no compromise and traced the blacklisting to the brand's own ad campaign and an abandoned tracker.

Read Details