Case Study: Thirty Sites, Two Keys
A marketing agency's WordPress sites kept serving fake Cloudflare prompts and gambling spam after repeated cleanups. Unrevoked hosting access and stolen admin credentials explained the reinfections.
Read Details
A marketing agency's WordPress sites kept serving fake Cloudflare prompts and gambling spam after repeated cleanups. Unrevoked hosting access and stolen admin credentials explained the reinfections.
Read Details
A law firm's WordPress site kept getting reinfected with ClickFix malware after every professional cleanup. The root cause was not a self-healing virus. It was a valid administrator login that was never rotated. Here is the full investigation.
Read Details
A boutique advisory client's two WordPress sites were compromised through administrator access left over from the freelancer who built them: rogue admin accounts, gambling spam, and a file-manager backdoor. A full forensic remediation evicted the operator and cleaned and hardened both sites.
Read Details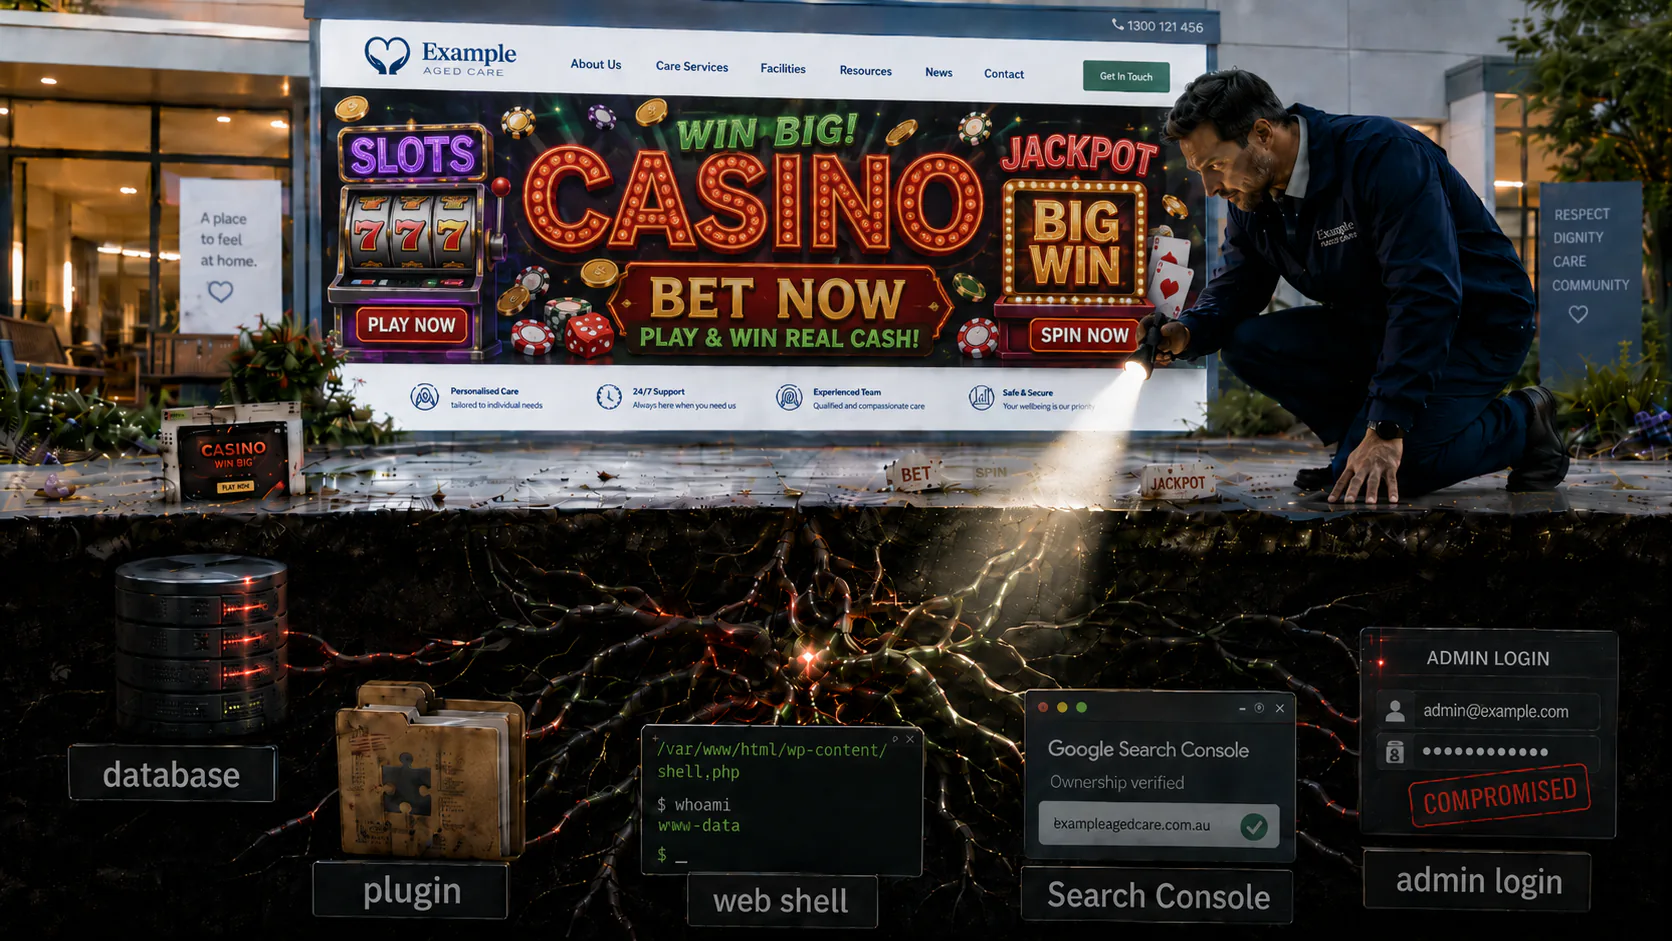
An aged-care provider's WordPress site kept reinfecting after prior cleanups, with gambling spam and Search Console hijacks returning. The cause was database malware, two backdoors, and a stolen admin credential.
Read Details
How WordPress sites actually get hacked, what malware does once it's in, what cleanup means, and how to tell whether the advice you're getting is sound. Written for owners who run their own site and for owners working with a developer or agency.
Read Details
WordPress malware cleanup pricing in 2026, broken down by real-world scenarios. What straightforward cleanups cost, what serious compromises cost, and what changes the number.
Read Details
If your site has been hacked and you've found a suspicious file, deleting it is often the wrong first move. Here's why — and what to do instead.
Read Details